Access reviews and audit evidence
Prove access is right. Any day, not just audit week.
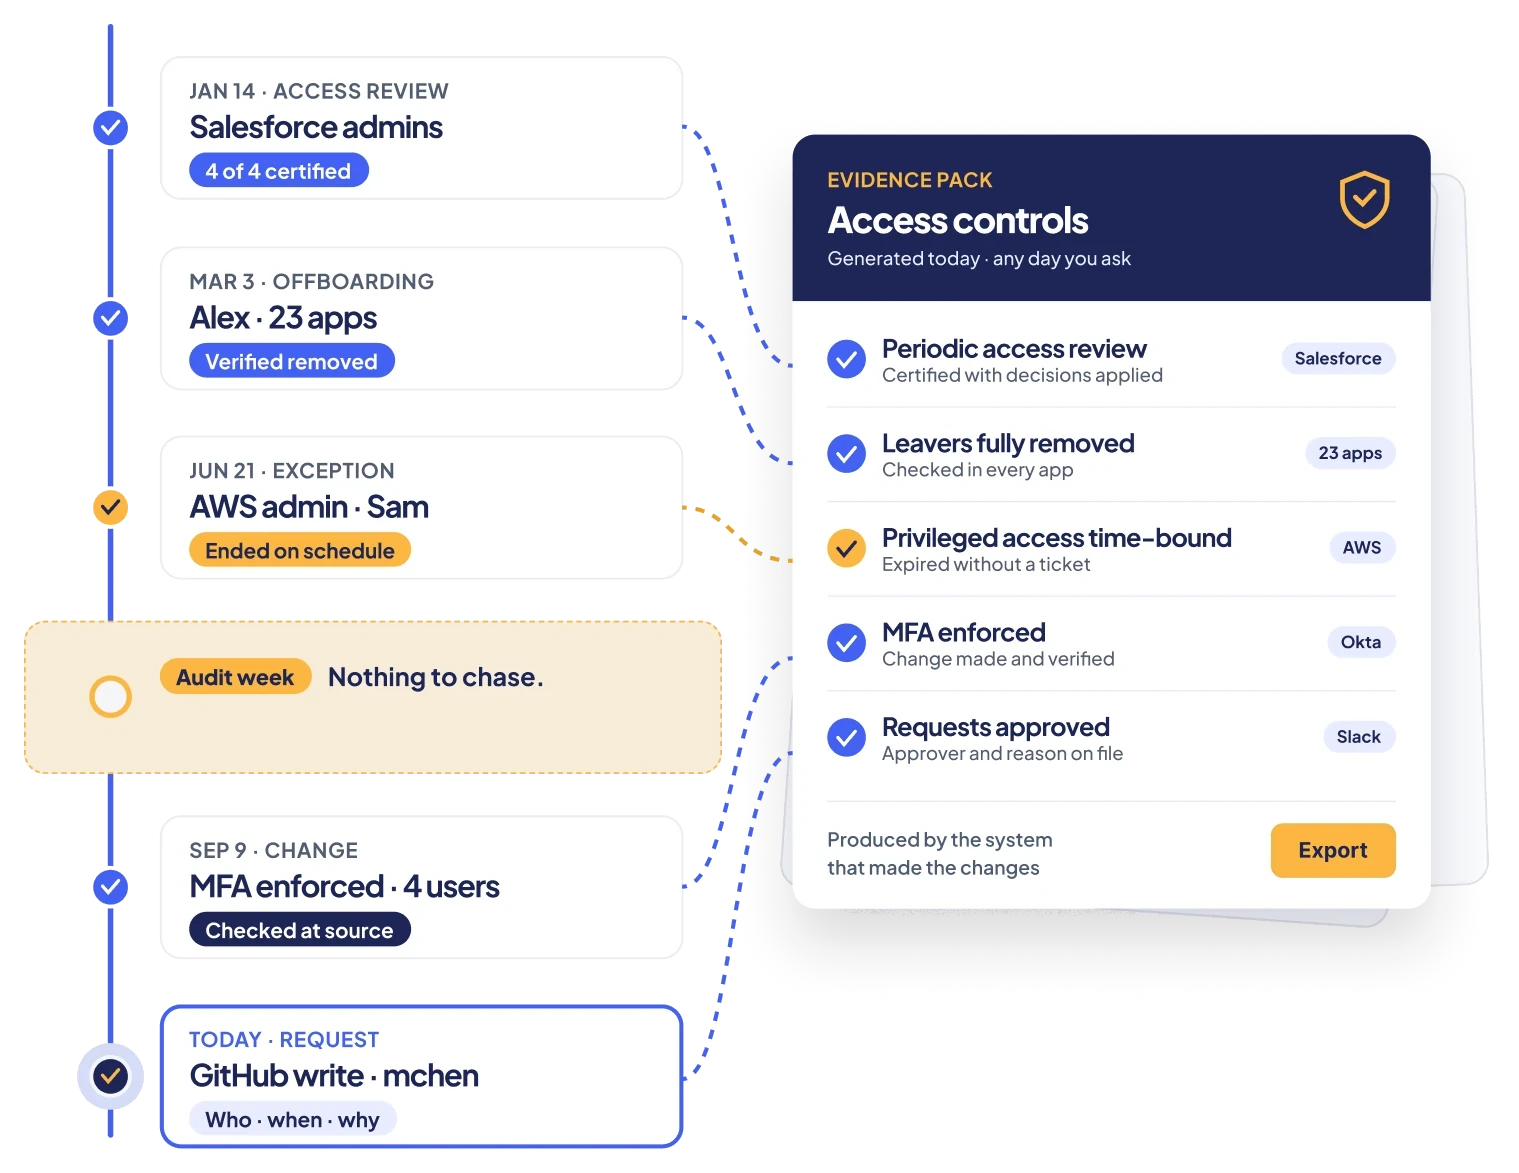
Access reviews, offboarding validation and evidence, produced by the system that actually made the changes.
Access reviews and audit evidence
Access reviews, offboarding validation and evidence, produced by the system that actually made the changes.
The problem
Auditors ask three things.


Reviewers get 400 lines they can't interpret, approve them all, and nothing changes.
Prove Access Capabilities

Built on effective access, so reviewers see what they're approving.

Scheduled or on demand, by app, team, role or risk.

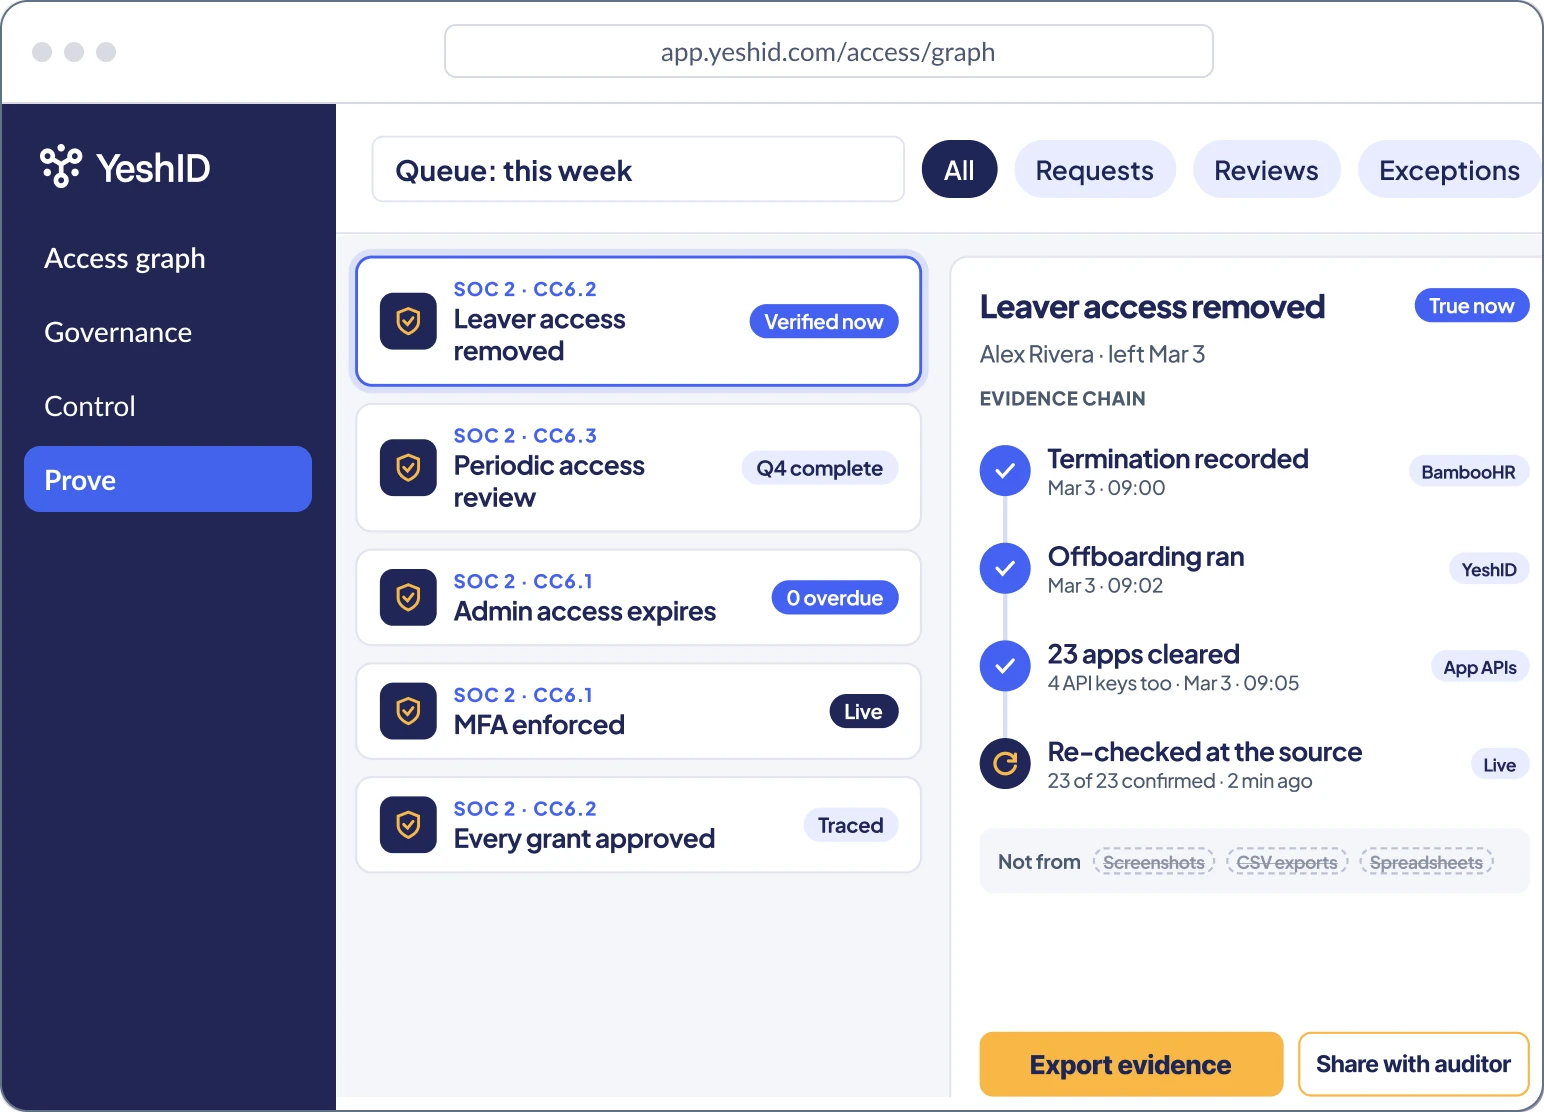
Proof a departed user's access is gone everywhere, confirmed at the source.

Every request, approval, change and exception, captured as it happens.

Who had access to what on any date.

Where access broke policy, for how long and how it was resolved.

Mapped to SOC 2, ISO 27001 and the frameworks your auditors use.
How it works
Every access decision is logged when it happens.
Each line shows what the access grants, when it was last used and whether it fits policy. Unused and out-of-policy access comes first.
“Remove” doesn't become a ticket. It goes to Control Access and gets verified.
Export evidence by control, framework, period, app or identity.
Use cases


Hand auditors evidence from the system of record, not a folder of screenshots.
Run inside YeshID, with reviewers who know what they're approving.
The full trail for one departed employee, in seconds.
What an account could reach on the day it was compromised.
Answer access-control questions with real data.
Most compliance evidence is rebuilt after the fact. YeshID's evidence is the record of access being granted, changed and removed.
Decisions flow into enforcement and get verified, so a certification reflects what's true afterward.
Vanta, Drata and Secureframe get you compliant. YeshID keeps your access controls working between audits.
Something else on your mind? Talk to our team.
Prove Access is YeshID's evidence layer: access reviews, certifications and audit records produced by the system that granted, changed and removed the access.
A user access review is a periodic check that each person, service account and AI agent still needs the access they have. YeshID runs them on live effective access and carries out the removals.
No. They track your compliance program. YeshID runs the access controls and produces the evidence.
Access evidence for SOC 2 and ISO 27001, plus any framework that asks who has access, who approved it and when it was removed.
Yes. See who had access to what on any date.
No. Reviews are built for managers and app owners, not identity specialists.
Yes. Service accounts, OAuth apps and AI agents are reviewed and certified like people.
A record of every access decision, strong enough to hand an auditor.