Just-In-Time Access
Just-in-time accesswithout permanent privilege creep
Grant temporary access across automated and non-automated applications, enforce eligibility through policy, and revoke or de-escalate privileges automatically.
Just-In-Time Access
Grant temporary access across automated and non-automated applications, enforce eligibility through policy, and revoke or de-escalate privileges automatically.
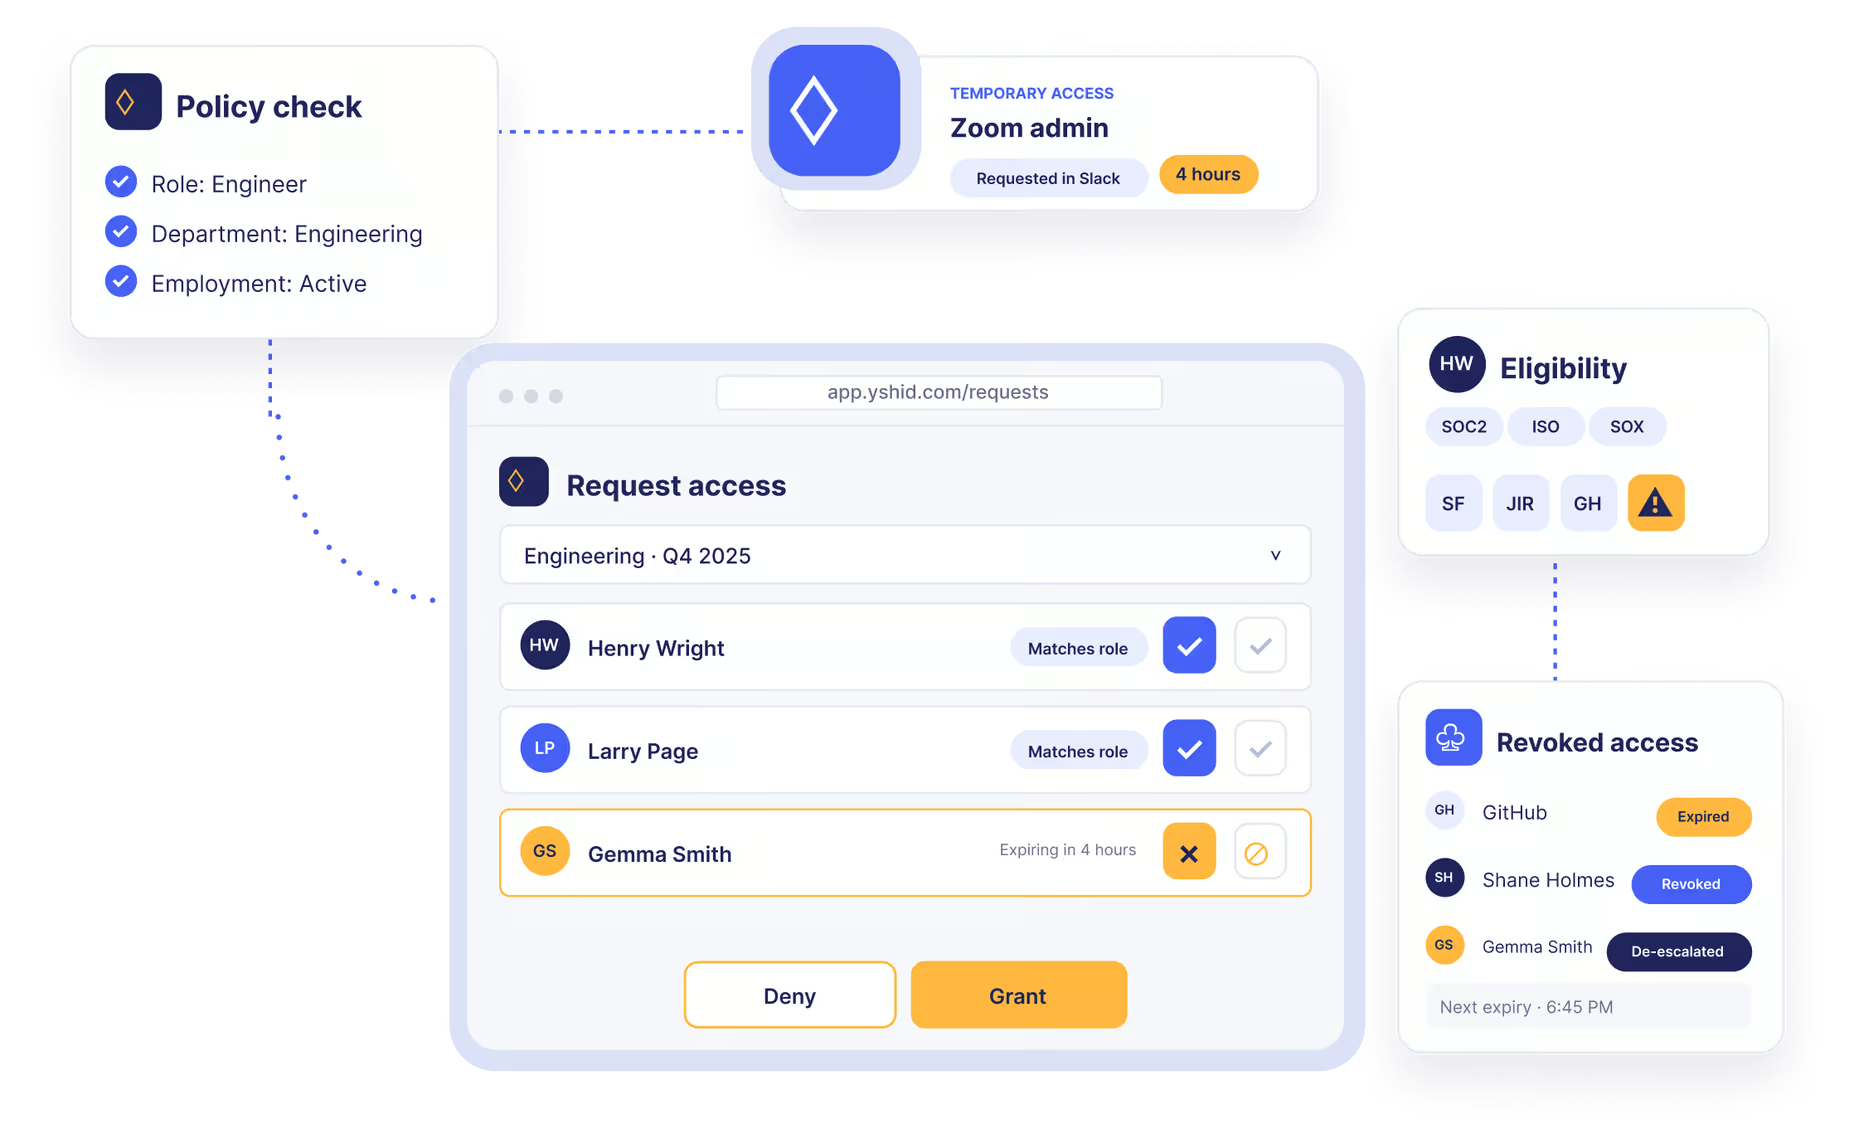
YeshID treats just-in-time access as a controlled lifecycle event. Temporary access is granted based on policy, enforced across both automated and manual systems, and revoked when conditions change.
Users can only request just-in-time access if policy allows it. If a role, attribute, or employment state should never permit access, the request cannot be made.
Every just-in-time grant includes a defined duration. When the window expires, YeshID revokes access or reduces privileges back to the approved baseline.
For applications that support automation, YeshID enforces access changes directly. For systems that do not, YeshID tracks, flags, and governs access so manual gaps do not become invisible risk.
Just-in-time access is handled separately from baseline roles and groups, preventing short-term needs from permanently altering access models.
YeshID shows where temporary access is repeatedly granted, whether it was properly removed, and where “temporary” access has effectively become permanent drift.
Find out what your people and software can really reach.